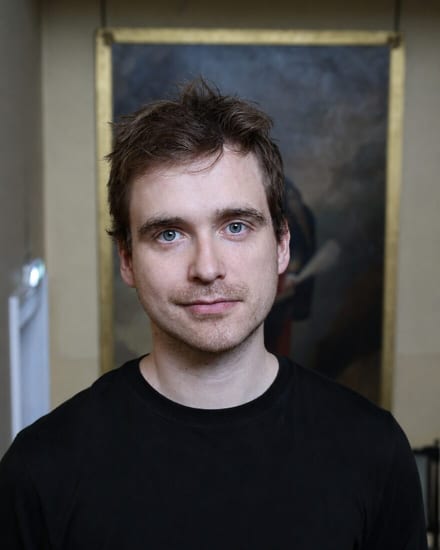
Security researcher and founder of Accretion, with four years auditing Solana programs. The security mind behind hackhack: what the engine looks for, and how it decides a bug is real.
Run a security review today. Get verified findings in a few hours, without waiting weeks for an auditor. Built for Anchor, native Rust, and Pinocchio.
Confirmed findings from Solana security reviews and bug bounty research. Every entry below was validated locally.
| Detected | ID | Severity | Source | Verified | Target | Finding |
|---|---|---|---|---|---|---|
| 2026-04-01 | HH-4195 | critical | customer | ✓ | aggregator | An adapter leaked the protocol signer to a chosen program |
| 2026-03-13 | HH-4013 | high | bounty | ✓ |  Jupiter | A denial of service locked users in borrow/lend positions |
| 2026-03-31 | HH-4161 | critical | customer | ✓ | aggregator | Fake deposits, real withdrawals |
| 2026-02-27 | HH-3948 | critical | bug hunt | ✓ |  Ellipsis (Phoenix) | An unauthenticated transfer let anyone move user collateral |
| 2026-03-31 | HH-4159 | critical | customer | ✓ | aggregator | Cancel your withdrawal, drain someone else’s escrow |
| 2026-04-15 | HH-4361 | high | customer | ✓ | vault | A liquidator could force a trade on a healthy account |
| 2026-03-28 | HH-4128 | high | customer | ✓ | gated token | A wrapper hid a transfer outside the signed envelope |
| 2026-03-28 | HH-4122 | high | customer | ✓ | gated token | One signature approved two different instruction streams |
| 2026-03-31 | HH-4155 | high | customer | ✓ | aggregator | A public swap spent ten times the approved amount |
| 2026-04-15 | HH-4368 | high | customer | ✓ | vault | A refund pool paid one user out of another’s deposit |
Every reported finding goes through our verification pipeline. We check whether the issue is real and what it means for your protocol, so you can spend your time fixing bugs with a clear understanding of why they matter.
The bug, the affected code, its impact, and the reasoning behind the finding. Enough context to understand the issue and work on the fix.
We measure recall against findings that senior auditors confirmed on the same code. hackhack is not a replacement for a human review. It is the layer that gets you most of the way there before one starts.
Recall against a fixed corpus of previously disclosed Solana vulnerabilities. Human-auditor recall is the 100% baseline.
 the pre-audit engine
Every Accretion engagement starts with a hackhack pre-audit across the customer’s repositories. The machine clears what a machine can clear, so senior auditors spend their time where human judgement actually matters.
The pre-audit clears the mechanical findings before a human auditor opens the repository, so the engagement starts further along.
The engagement is spent on design, economics and intent, not on the bugs a machine had already found.
Routine issues are gone before the report is written, so what is left in it is the substance.
The simple bugs are fixed before the audit starts, which cuts rounds off remediation at the end.
You get a better audit, not a thinner one.
Anchor, native Rust, or Pinocchio. Whatever you are shipping.
An autonomous review with verified findings your team can fix before the audit.
Senior auditors start on the hard part: design, economics, intent.
Start today, without an audit engagement, an introduction, or a sales call. Submit your repository and get verified findings in a few hours.
Run a security reviewIncluded as the pre-audit layer in every Accretion audit. Submit a review here first and book an audit later, and what you spent here is credited against that engagement, up to the cap.
hackhack is built by people who find bugs for a living, with a wider team of engineers and researchers behind them. The engine encodes how we audit Solana programs by hand, which is why it looks for the things that actually break protocols.
Security researcher and founder of Accretion, with four years auditing Solana programs. The security mind behind hackhack: what the engine looks for, and how it decides a bug is real.
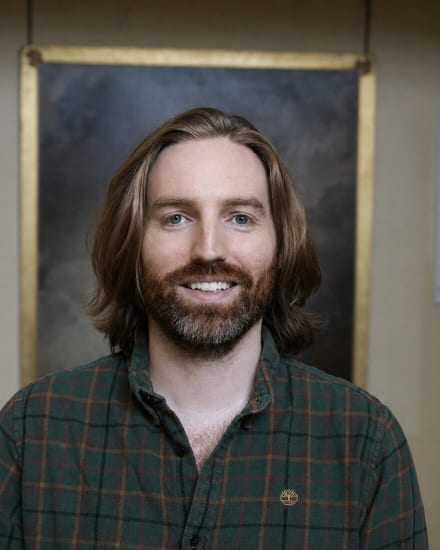
AI researcher with a PhD in deep learning, and an engineer first. Has built at Backpack, Anchor, MetaDAO and Marginfi. The brain behind the models and the evaluation engine.
Buy tokens and start a review whenever you need one. Before a release, after a fix, or while you build. Every run includes the same verification pipeline, with results in a few hours.
One program, one review. How most teams start.
An initial run, a re-run on your fixes, and a final review.
Continuous coverage through an active dev cycle. Security you can plan around.
No waiting weeks for an auditor’s calendar to clear. Run hackhack on your time and get real, verified findings in a few hours.
Run a review today